INCIDENT RESPONSE READINESS // GRIDHEART MSP

    03:14 on Sunday morning.

    The phone rings. It's your biggest customer. Everything is down. The screens show this:
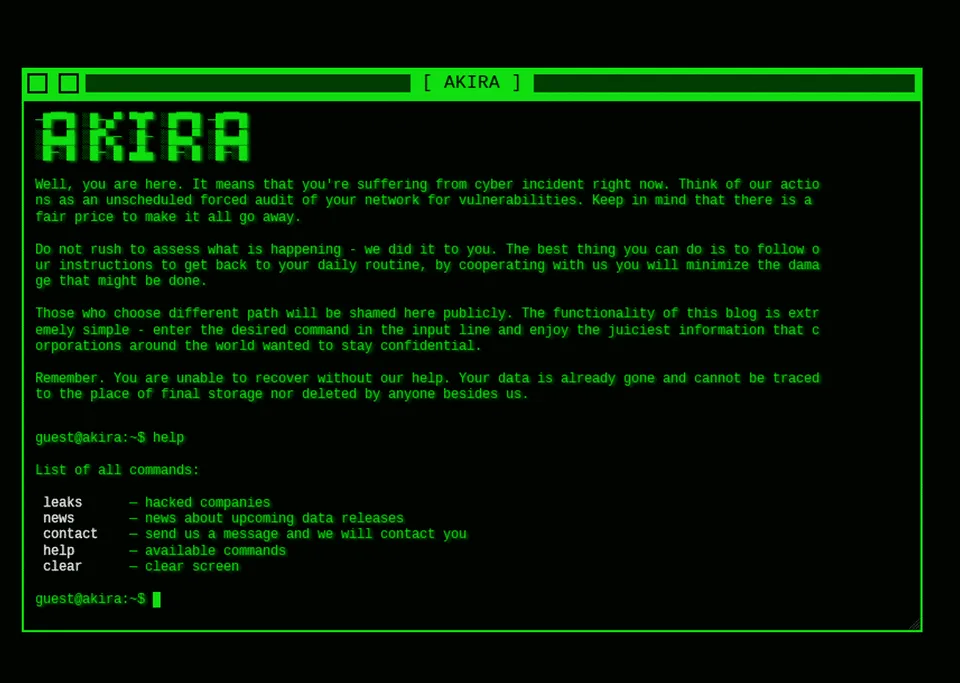
    Do you know what to do?

    Do you have the situation under control - or are you improvising in panic?

    15 questions. 6 phases. From the first call to the aftermath.
    Honest answers - no one sees them but you.

    This is not a drill. Akira has attacked 250+ Nordic companies since 2023.

    Gridheart // Ransomware Playbook

    What you do at 03:14. When everything is encrypted.

    Free playbook

    Screenshot of the Akira ransomware group's terminal screen. Green monospace text on a black background with the AKIRA title in pixel art. The text reads: Well, you are here. It means that you're suffering from cyber incident right now. Think of our actions as an unscheduled forced audit of your network for vulnerabilities. Keep in mind that there is a fair price to make it all go away. Do not rush to assess what is happening - we did it to you. The best thing you can do is to follow our instructions to get back to your daily routine. Those who choose different path will be shamed here publicly. Remember. You are unable to recover without our help. Your data is already gone. Below is a command list: leaks, news, contact, help, clear.

    The Ransomware Playbook for MSPs

    A practical, step-by-step guide for the first 72 hours of an active ransomware incident. Built with Nordic IRT specialists. Available for SE, UK and EU.

    Choose your region