INCIDENT RESPONSE READINESS // GRIDHEART MSP

    03:14 sunnuntaiaamuna.

    Puhelin soi. Se on suurin asiakkaasi. Kaikki on nurin. Näytöillä lukee tämä:
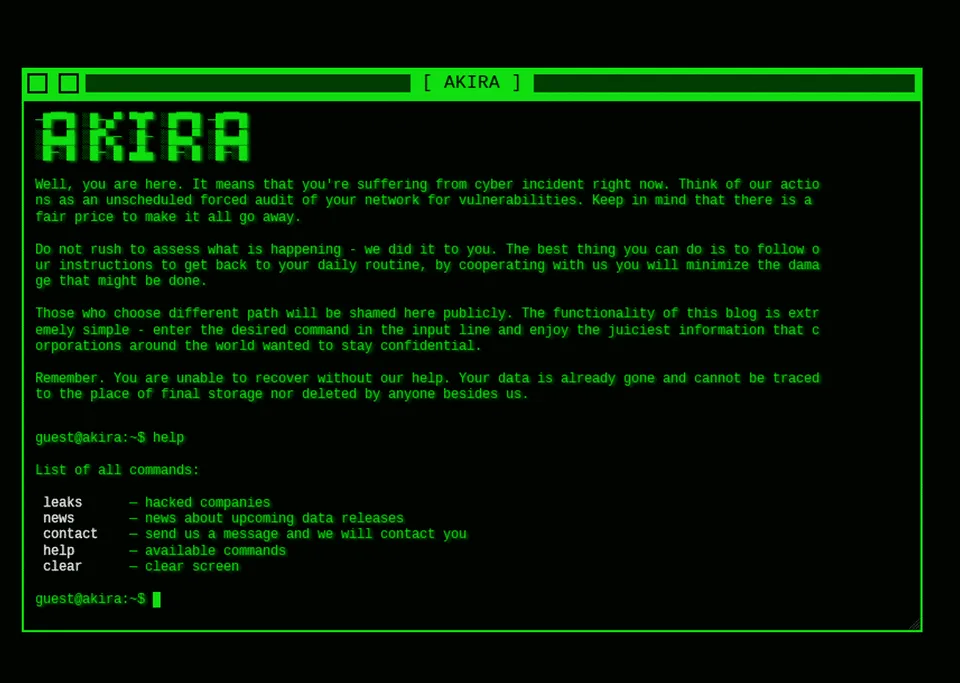
    Tiedätkö mitä tehdä?

    Onko tilanne hallinnassasi - vai improvisoitko paniikissa?

    15 kysymystä. 6 vaihetta. Ensimmäisestä puhelusta jälkiselvitykseen.
    Rehelliset vastaukset - kukaan muu ei näe niitä kuin sinä itse.

    Tämä ei ole harjoitus. Akira on hyökännyt yli 250 pohjoismaista yritystä vastaan vuodesta 2023 lähtien.

    Gridheart // Ransomware Playbook

    What you do at 03:14. When everything is encrypted.

    Free playbook

    Kuvakaappaus Akira-kiristysohjelmaryhmän terminaalinäytöstä. Vihreä monospace-teksti mustalla taustalla otsikolla AKIRA pikselitaiteella. Teksti kuuluu: Well, you are here. It means that you're suffering from cyber incident right now. Think of our actions as an unscheduled forced audit of your network for vulnerabilities. Keep in mind that there is a fair price to make it all go away. Do not rush to assess what is happening - we did it to you. The best thing you can do is to follow our instructions to get back to your daily routine. Those who choose different path will be shamed here publicly. Remember. You are unable to recover without our help. Your data is already gone. Alla on komentolista: leaks, news, contact, help, clear.

    The Ransomware Playbook for MSPs

    A practical, step-by-step guide for the first 72 hours of an active ransomware incident. Built with Nordic IRT specialists. Available for SE, UK and EU.

    Choose your region