INCIDENT RESPONSE READINESS // GRIDHEART MSP

    03:14 Uhr am Sonntagmorgen.

    Das Telefon klingelt. Es ist Ihr größter Kunde. Alles liegt brach. Auf den Bildschirmen steht Folgendes:
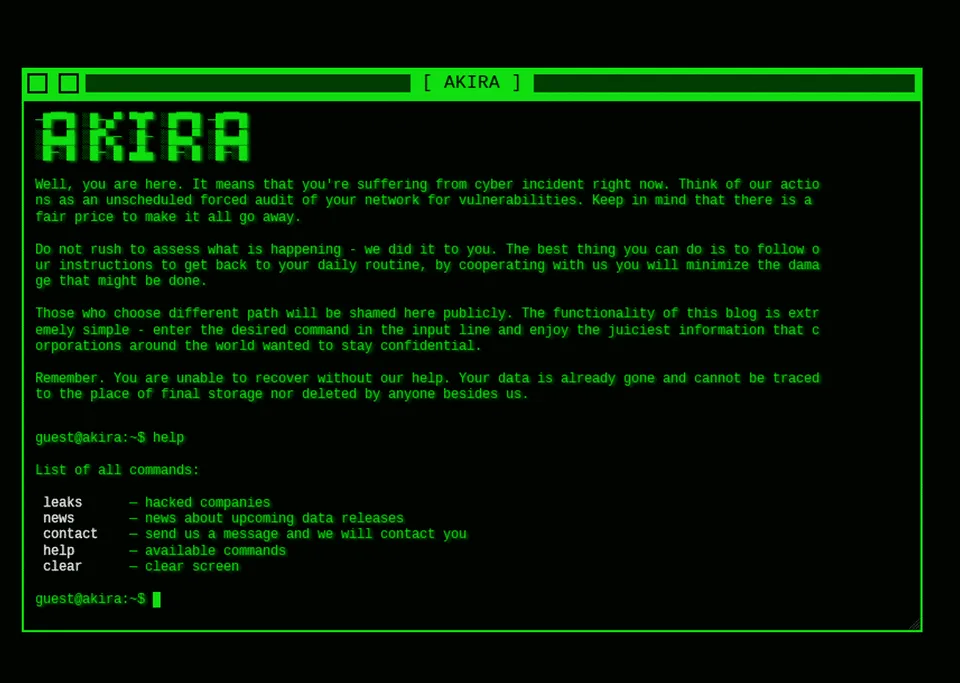
    Wissen Sie, was zu tun ist?

    Haben Sie die Situation unter Kontrolle - oder improvisieren Sie panisch?

    15 Fragen. 6 Phasen. Vom ersten Anruf bis zur Nachbereitung.
    Ehrliche Antworten - niemand außer Ihnen wird sie sehen.

    Dies ist keine Übung. Akira hat seit 2023 über 250 nordische Unternehmen angegriffen.

    Gridheart // Ransomware Playbook

    What you do at 03:14. When everything is encrypted.

    Free playbook

    Screenshot des Terminalbildschirms der Akira-Ransomware-Gruppe. Grüner Monospace-Text auf schwarzem Hintergrund mit der Überschrift AKIRA in Pixelkunst. Der Text lautet: Well, you are here. It means that you're suffering from cyber incident right now. Think of our actions as an unscheduled forced audit of your network for vulnerabilities. Keep in mind that there is a fair price to make it all go away. Do not rush to assess what is happening - we did it to you. The best thing you can do is to follow our instructions to get back to your daily routine. Those who choose different path will be shamed here publicly. Remember. You are unable to recover without our help. Your data is already gone. Darunter eine Befehlsliste: leaks, news, contact, help, clear.

    The Ransomware Playbook for MSPs

    A practical, step-by-step guide for the first 72 hours of an active ransomware incident. Built with Nordic IRT specialists. Available for SE, UK and EU.

    Choose your region