PREPARAÇÃO PARA RESPOSTA A INCIDENTES // GRIDHEART MSP

    03:14 de domingo de manhã.

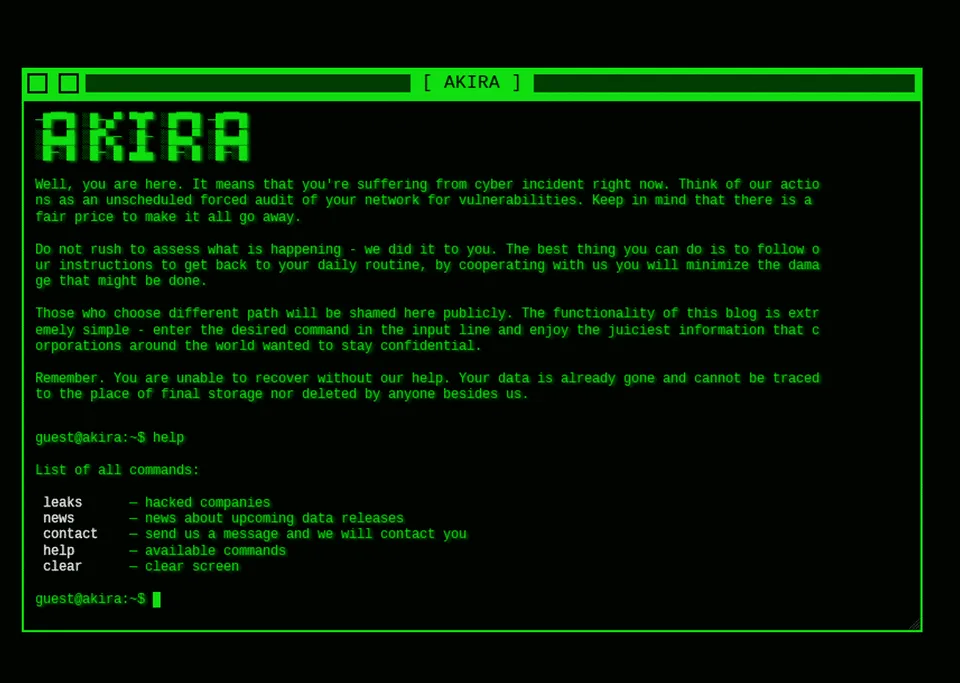
    O telefone toca. É seu maior cliente. Tudo está inativo. Nas telas, aparece isto:
    Você sabe o que fazer?

    Você tem a situação sob controle - ou está improvisando em pânico?

    15 perguntas. 6 fases. Da primeira ligação ao rescaldo.
    Respostas honestas - ninguém as vê além de você mesmo.

    Isto não é um exercício. Akira atacou mais de 250 empresas nórdicas desde 2023.

    Gridheart // Ransomware Playbook

    What you do at 03:14. When everything is encrypted.

    Free playbook

    Captura de tela da tela do terminal do grupo de ransomware Akira. Texto verde monospace em fundo preto com o título AKIRA em pixel art. O texto diz: Well, you are here. It means that you're suffering from cyber incident right now. Think of our actions as an unscheduled forced audit of your network for vulnerabilities. Keep in mind that there is a fair price to make it all go away. Do not rush to assess what is happening - we did it to you. The best thing you can do is to follow our instructions to get back to your daily routine. Those who choose different path will be shamed here publicly. Remember. You are unable to recover without our help. Your data is already gone. Abaixo, há uma lista de comandos: leaks, news, contact, help, clear.

    The Ransomware Playbook for MSPs

    A practical, step-by-step guide for the first 72 hours of an active ransomware incident. Built with Nordic IRT specialists. Available for SE, UK and EU.

    Choose your region