The freezer attacks - when control systems become the target
How the attack worked
The attack targeted refrigeration controllers from the Danish manufacturer Danfoss, specifically the older AK-SM 800 and AK-SC 355 units. The attackers put the evaporators into defrost mode and left them running all night, with temperature settings of up to 50 degrees Celsius. In several cases, staff on site were unable to restore the settings, and chilled and frozen goods had to be discarded. Sweden's National Cyber Security Centre, part of the National Defence Radio Establishment (FRA), is assisting with the response.
Beyond Sweden, attacks were reported the same night in Belgium, Ireland, the Netherlands, Luxembourg, Estonia and Finland. The pattern was the same everywhere: controllers that could be reached from outside and manipulated without anyone noticing until the morning.
One detail stands out from an IT perspective. At one of the large Swedish chains, the affected sites were connected outside the group's central network, meaning outside the environment the IT department monitors. The same type of control system is found in restaurants, commercial kitchens, butchers and smaller food businesses, often installed by a refrigeration technician and then left alone for years.
A second wave in three weeks
The November attacks repeated a series of earlier ones. On 12 October, around 700 stores in France were hit in exactly the same way, against the same controllers. The French CERT-FR issued warnings and recommendations within days, and Danfoss urged customers to review their installations.
The threat was known, the method was known, and the manufacturer had given clear advice. Even so, enough sites remained exposed for the next wave to hit seven countries three weeks later. That says less about the attackers' capabilities and more about how hard it is to act on a warning when no one clearly owns the equipment.
For Swedish businesses, this comes as requirements are tightening. The new Swedish Cybersecurity Act and NIS2 cover food production and distribution, and more companies will now be expected to show that they are in control of their systems, including the ones sitting in a plant room behind the freezer aisle.
Why the controllers were so easy to reach
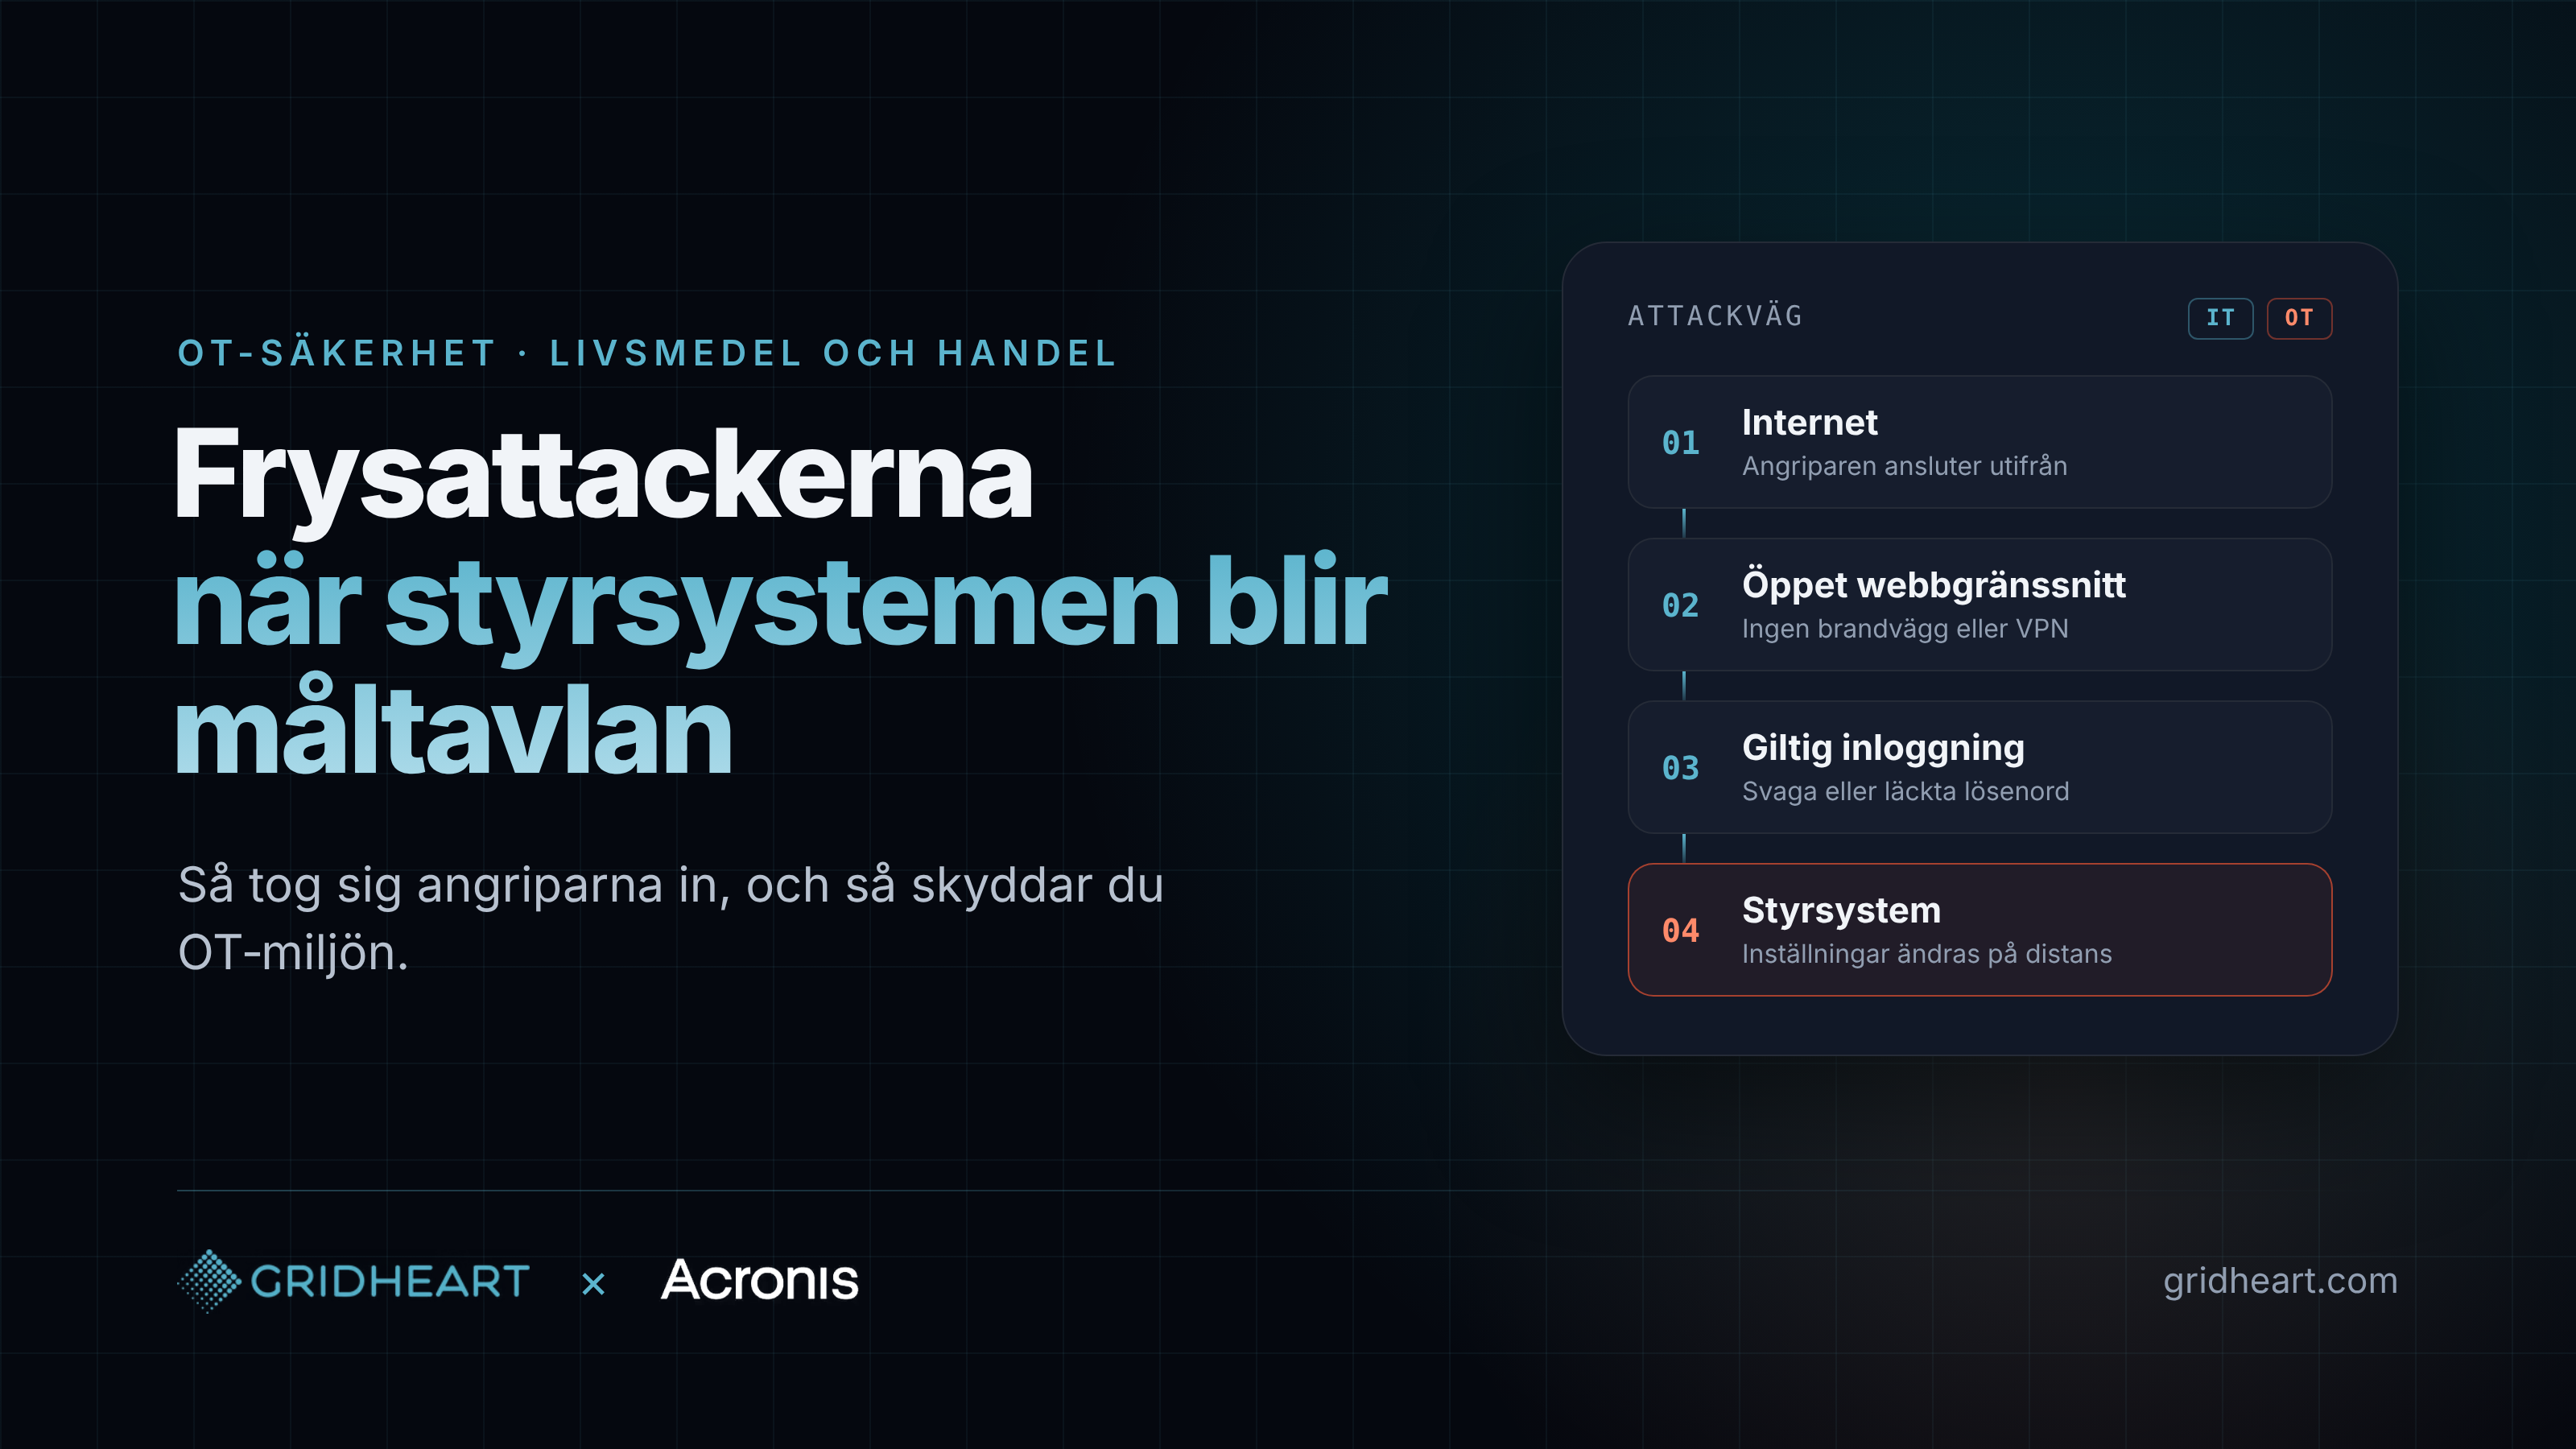
The attackers needed no advanced vulnerability to carry out these attacks. According to reporting from France and Belgium, the controllers were reached through web interfaces exposed directly to the internet, using login credentials that gave full control. No software vulnerability has been linked to the attacks, and they require little technical skill to carry out.
Three things make refrigeration control an attractive target. The equipment has a long life: the AK-SM 800 has been out of production since 2021 and the AK-SC 355 since 2016, and neither receives security updates any more. It is often installed and maintained by an external service partner who needs remote access, which easily ends in an open port and a shared password. And it rarely makes it into the IT department's inventory, because it is seen as part of the building rather than the network.
That pattern is not unique to refrigeration. Ventilation, access control, energy metering and production equipment in smaller food businesses share the same history, and therefore the same exposure.
An OT attack with an IT entry point
What was knocked out was OT, but the way in was classic IT. Web interfaces exposed to the internet, login credentials that worked, remote access without individual accounts or multi-factor authentication, and equipment with no segmentation from the rest of the network. None of these weaknesses is specific to refrigeration control. It is the same basic IT hygiene that applies to a server or a firewall.
The difference is that the equipment has fallen between the cracks. The IT department sees refrigeration as part of the building, the refrigeration technician sees it as a machine, and neither has overall responsibility for the fact that it is connected. In practice, OT equipment sits on the same network, is reached over the same internet and is protected by the same kind of passwords as everything else. So it also needs to be covered by the same routines for inventory, access control, monitoring and recovery.
For an MSP, this is a natural extension of the job. You are already responsible for the customer's network, firewalls, remote access and backup. Bringing refrigeration control, ventilation and other connected technology into the same overview does not require building new expertise from scratch. It means starting to count them as part of the environment you protect.
How to reduce the risk
Start by finding out what is actually there. Make a list of every controller for refrigeration, ventilation and other building or production technology, with model and firmware version, and ask the service partner how they connect. Many discover at this stage that the equipment can be reached from the internet.
Then remove the direct exposure. Both Danfoss and CERT-FR are clear that control systems should not be exposed to the internet. Remote access should go through a VPN or a protected jump host, with individual accounts per user and multi-factor authentication where possible. Change default and shared passwords, and separate OT equipment from the office network and point-of-sale systems with a firewall.
Also plan for something going wrong anyway. For equipment that can no longer be updated, an independent temperature alarm that does not run through the same control system is a cheap way to detect an attack before the goods are ruined. And for the computers and servers that monitor and control the site, there needs to be a ready path back to a known good state.
Where Acronis Cyber Protect for OT fits in
A refrigeration controller is an embedded device, and the first line of protection is making sure it cannot be reached from outside. But around it there are often Windows and Linux machines that monitor, control and log: monitoring PCs, HMI stations, SCADA servers and the jump servers service partners use to connect. This is where Acronis Cyber Protect for OT makes a difference.
The solution takes full image backups of these systems without stopping production, and on-site staff can restore them with a single click. It supports legacy operating systems such as Windows XP and Server 2003, which are still common in OT environments, and can run fully disconnected from the network. The same agent provides protection against malware and ransomware, vulnerability assessment, patch management and inventory, so you get both an overview of what is there and a fast way back if something is tampered with. Acronis is also certified to IEC 62443-4-1, the standard for secure development of industrial systems.
At Gridheart, our OT team works with MSPs that want to take care of exactly this kind of environment for their customers. Many of your customers in retail, hospitality and food have OT equipment that no one really owns today. With Acronis Cyber Protect for OT, you as an MSP can offer concrete protection for those systems, from the same vendor many MSPs already use for IT protection.
Next steps
The freezer attacks show how thin the margins are when OT is left unattended. One open port and one leaked password were enough to destroy goods worth millions across several countries in a single night. The good news is that most of the measures are well known and can be put in place right now.
Want to know more about Acronis Cyber Protect for OT, or how you can build an OT offering for your customers? Get in touch at sales@gridheart.com.